📡 PwnBox // Imp Info
// TACTICAL HARDWARE IMPLANTS & CYBERSPACE INTELLIGENCE

HACKER SEARCH ENGINES & TACTICAL HARDWARE DEVICES

Knowledge is Power. Hack the Planet (Ethically)! A unified classified compendium detailing the Top 10 Physical Penetration Testing Devices (Hak5, Flipper Zero, Proxmark3) alongside the 32 Essential Cybersecurity Search Engines for Internet-wide reconnaissance, exposed credentials, asset mapping, and threat intelligence.
Physical audit weaponry & global cyberspace reconnaissance engines.

01 Wireless & RF Pentesting
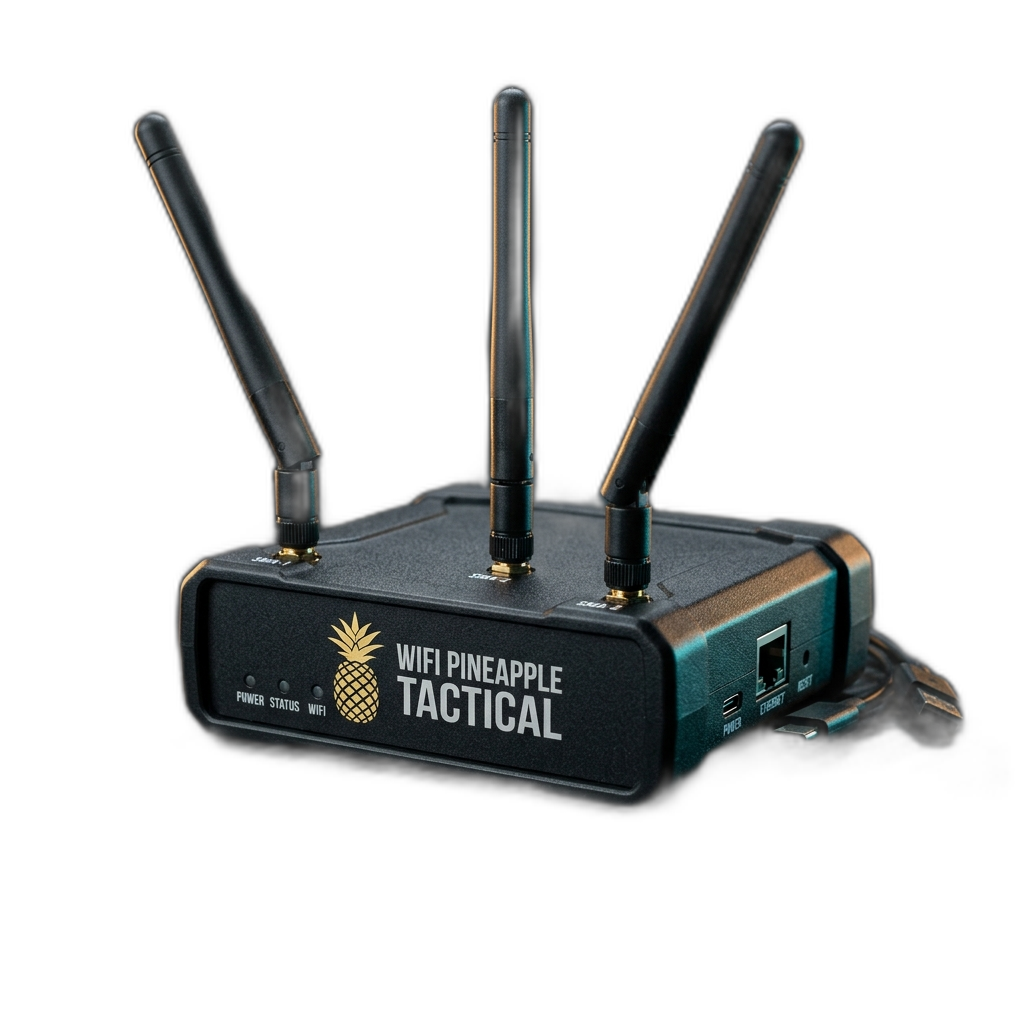
🌐 3D 360° ModelWiFi Pineapple

WiFi Pineapple

// Hak5
Powerful tool for Wi-Fi penetration testing. Intercept & analyze Wi-Fi traffic.

Dual-band (2.4GHz & 5GHz) tactical wireless audit platform. Employs the proprietary PineAP suite to automatically harvest client probe requests, launch Karma attacks, broadcast spoofed SSIDs, deauthenticate authenticated clients, and establish Man-in-the-Middle (MITM) control to capture WPA handshakes and harvest credentials.
Frequencies: 2.4 GHz & 5.8 GHz (Dual Band)
Core Engine: OpenWrt Linux / PineAP Suite
Key Attack: Rogue AP, Karma, Deauth, SSL Strip
⚡ Attack Vector
Clients connect to fake Wi-Fi; attacker intercepts traffic, forces captive portals, captures NTLM/HTTP credentials.
🛡️ Defense / Mitigation
Enforce 802.1X EAP-TLS enterprise Wi-Fi, enable WPA3 Protected Management Frames (PMF), forbid auto-connect to open SSIDs.
02 Mobile OSINT & HID
🌐 3D 360° ModelKali NetHunter

Kali NetHunter

// Offensive Security
Turn your Android phone into a hacking tool. Pentesting on the go!

Open-source Android mobile penetration testing overlay with custom kernel support. Delivers 802.11 wireless frame injection, AP mode, one-click HID keyboard attacks (DuckHunter BadUSB), USB Ethernet emulation (MANA Evil AP network hijacking), and Software Defined Radio (SDR) RF sniffing right from a pocket smartphone.
Platform: Android (Custom Linux Kernel)
Capabilities: 802.11 Injection, BadUSB, SDR, Bluetooth
Stealth Level: Maximum (Looks like standard smartphone)
⚡ Attack Vector
Walk into a facility unnoticed; connect via USB to inject HID payloads or passively sniff nearby RF/BLE/Wi-Fi traffic.
🛡️ Defense / Mitigation
Enforce strict Mobile Device Management (MDM), block USB OTG on enterprise workstations, physical device bans in server rooms.
03 Keystroke Injection (BadUSB)
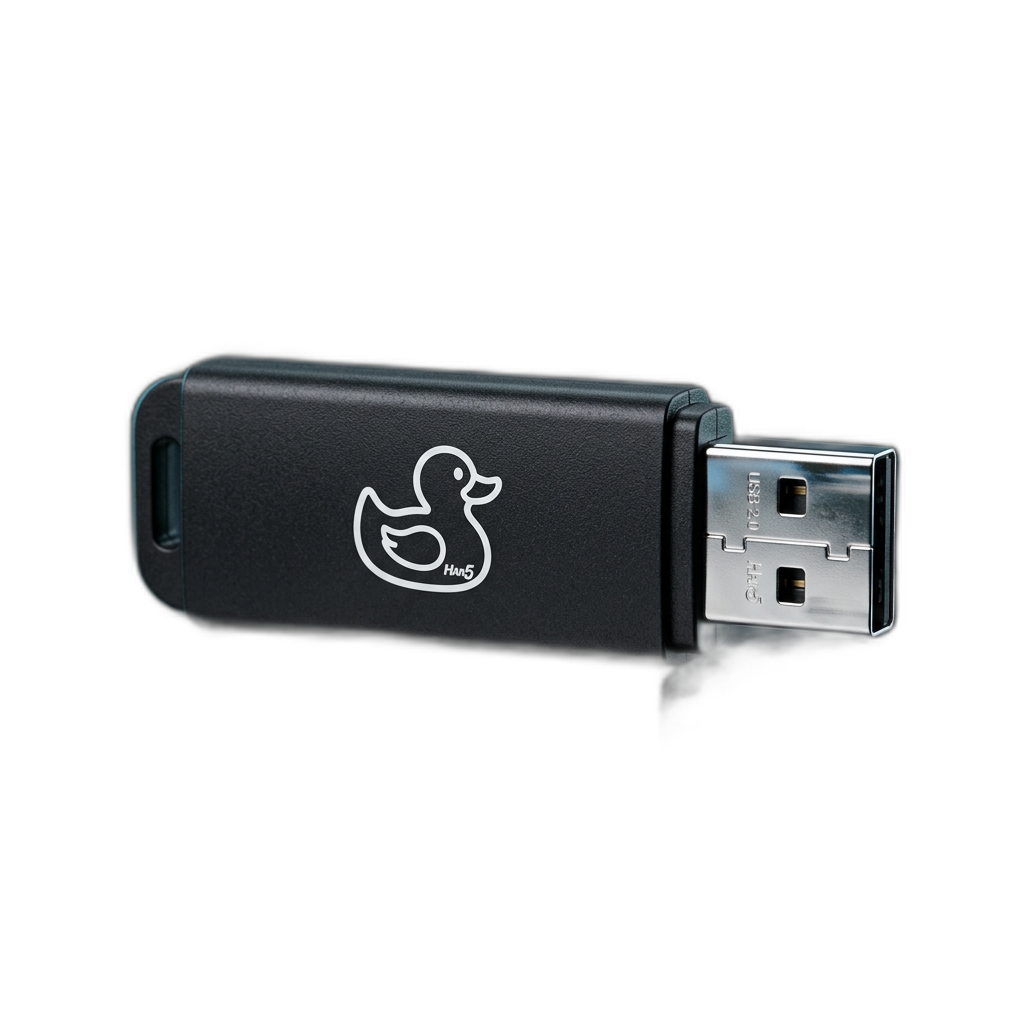
🌐 3D 360° ModelUSB Rubber Ducky

USB Rubber Ducky

// Hak5
Looks like a USB drive, acts like a keyboard. Automate attacks easily.

The definitive Human Interface Device (HID) keystroke injection platform. Because operating systems inherently trust keyboards without requiring driver installation or privilege prompts, the Rubber Ducky executes DuckyScript 3.0 at over 1,000 words per minute to open terminals, disable defenses, exfiltrate credentials, and deploy reverse shells in under 5 seconds.
Interface: USB-A / USB-C HID Emulation
Language: DuckyScript 3.0 (Logic, Conditionals, Jitter)
Speed: 1000+ words per minute injection
⚡ Attack Vector
Plugged into unattended laptop; immediately spawns PowerShell, downloads memory payload, exfiltrates Wi-Fi passwords to webhook.
🛡️ Defense / Mitigation
USB port allowlisting by Hardware VID/PID, physical USB port blocker locks, GPO restrictions on Command Prompt & PowerShell.
04 Multi-Vector Attack Platform
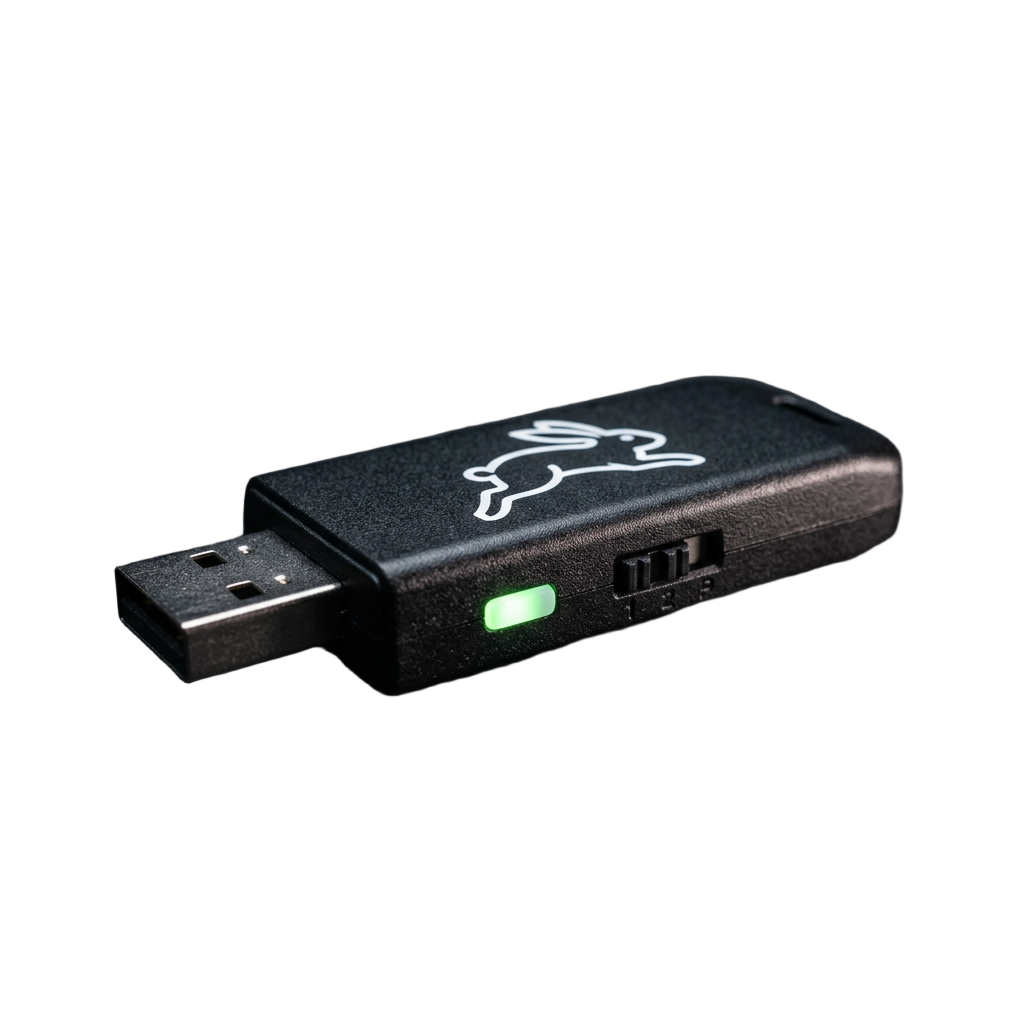
🌐 3D 360° ModelBash Bunny

Bash Bunny

// Hak5
Next-gen USB device for penetration testing. Run payloads & bypass security.

A complete Debian Linux computer built inside a USB stick form factor. Features a physical 3-position toggle switch allowing operators to execute distinct multi-vector payloads. Emulates Gigabit USB Ethernet (RNDIS/ECM), keyboard HID, USB Mass Storage, and Serial adapters simultaneously to poison LLMNR/NBT-NS hashes (QuickCreds) in seconds.
Operating System: Full Debian Linux Under the Hood
Hardware Toggle: 3-Position Switch (Payload 1, Payload 2, Arming)
Emulation: Gigabit Ethernet + HID + Flash Storage
⚡ Attack Vector
Pretends to be a fast Ethernet network card; Windows shifts default gateway, sends NTLMv2 challenge hashes; captures hashes instantly.
🛡️ Defense / Mitigation
Disable LLMNR and NetBIOS-NS via GPO, block installation of unauthorized RNDIS/Ethernet USB drivers, require admin approval for new NICs.
05 Sub-GHz, RFID & BadUSB
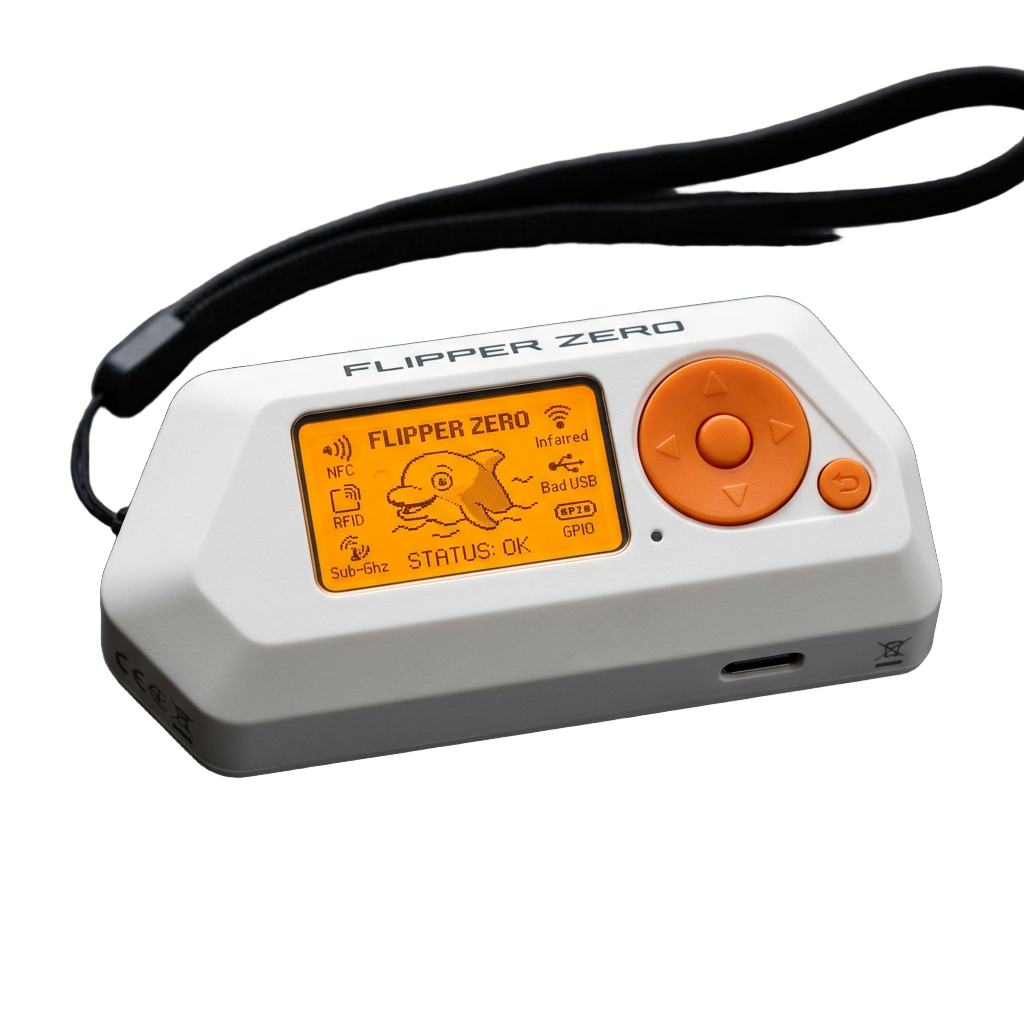
🌐 3D 360° ModelFlipper Zero

Flipper Zero

// Flipper Devices
Multi-tool for pentesters and geeks. Sub-GHz, RFID, NFC, Infrared, GPIO.

The viral multi-protocol hardware swiss army knife. Integrates a 300-928 MHz Sub-GHz transceiver for capturing and replaying wireless signals (garage doors, barrier gates), 125 kHz RFID reader/writer (EM4100, HID Prox door badges), 13.56 MHz NFC (Mifare Classic card emulation), Infrared blaster, BadUSB keystroke injector, and hardware GPIO pins.
RF Range: 300 MHz - 928 MHz (CC1101 Transceiver)
RFID / NFC: 125 kHz (LF) + 13.56 MHz (HF ISO-14443)
Hardware IO: Infrared TX/RX, 1-Wire, iButton, 18-Pin GPIO
⚡ Attack Vector
Clones building keycards with a touch; replays Sub-GHz barrier gate signals; plugs into unlocked PC to fire Ducky payloads.
🛡️ Defense / Mitigation
Upgrade legacy RFID badges to cryptographic credentials (Mifare DESFire EV3); enforce rolling-code anti-replay for physical gates.
06 Covert Network Implant
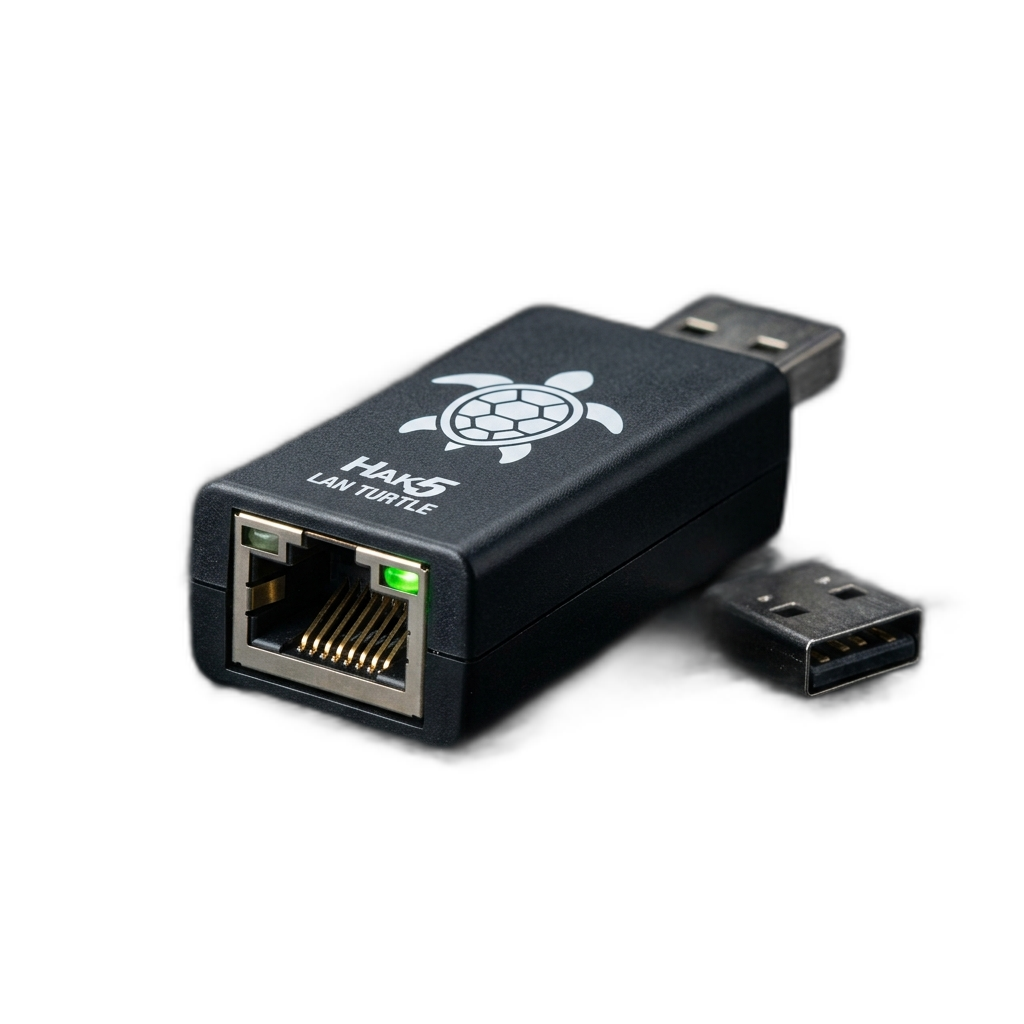
🌐 3D 360° ModelLAN Turtle

LAN Turtle

// Hak5
Disguised as a mobile charger/adapter, steals data.

A covert systems administration and penetration testing implant disguised as a generic USB-to-Ethernet adapter. Houses a customized OpenWrt embedded Linux kernel. Connects between a host computer and the local network to quietly sniff traffic, execute DNS poisoning (DNS Spoofing), and establish a persistent Cloud C2 reverse shell over cellular/VPN.
Architecture: Embedded OpenWrt MIPS Linux
Disguise: USB 2.0 to 10/100 Fast Ethernet Dongle
Features: Automated MITM, DNS2Proxy, SSH Reverse Shell
⚡ Attack Vector
Plugged into the back of a workstation; secretly intercepts all LAN traffic and maintains persistent out-of-band backdoor access.
🛡️ Defense / Mitigation
Network Access Control (802.1X NAC), 1-to-1 MAC port security on network switches, periodic physical audit of rear desktop I/O.
07 Covert Cable Implant
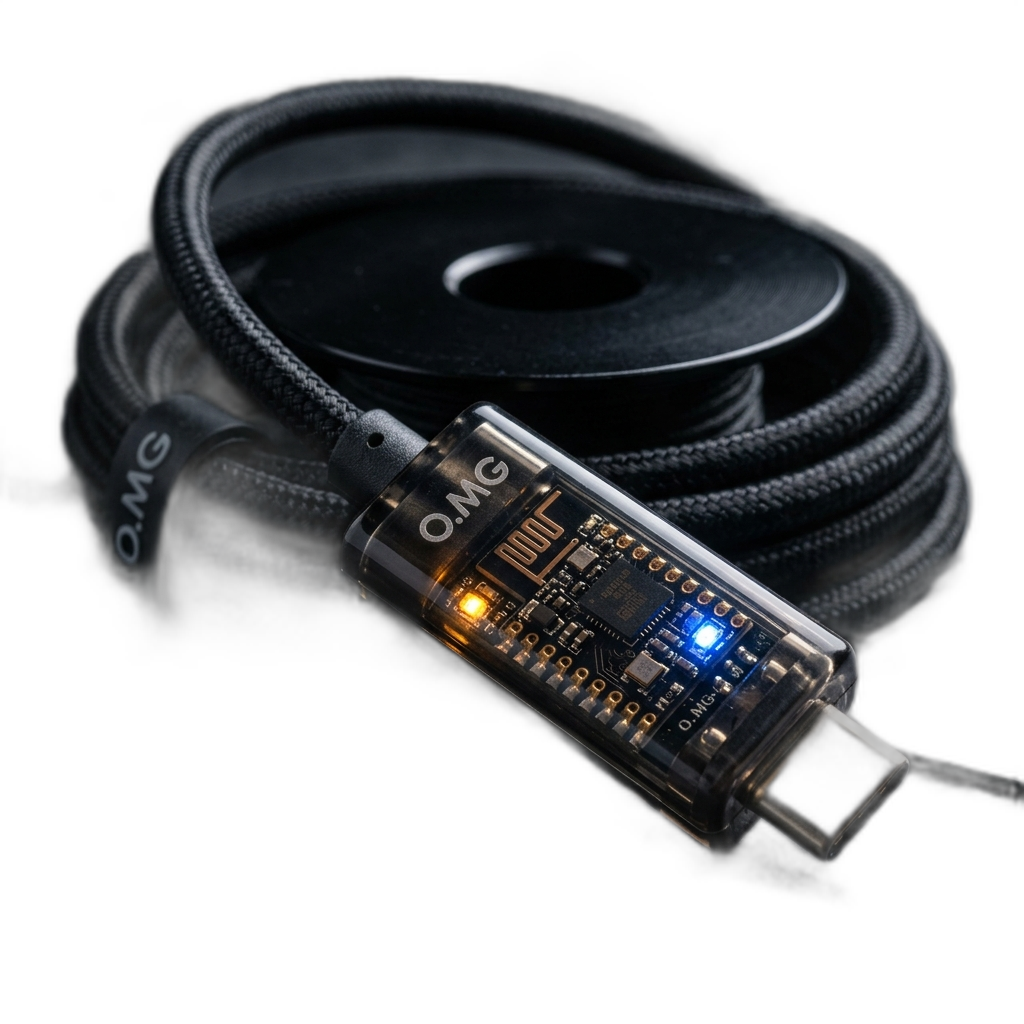
🌐 3D 360° ModelO.MG Cable

O.MG Cable

// Hak5 / MG
Bad USB cable for remote access attacks. Remote access in seconds.

Looks and behaves exactly like an authentic OEM smartphone charging cable (Apple Lightning, USB-C, Micro-USB). Concealed inside the molded connector housing is a tiny 32-bit microcontroller, full Wi-Fi radio, and web server. An attacker up to 50 meters away connects via smartphone browser to trigger keystrokes, log input, or drop payloads wirelessly.
Form Factor: 100% Indistinguishable Charging Cable
Remote Control: Concealed 802.11 b/g/n Wi-Fi AP + Web Server
Features: Air-gap bypass, keystroke logger, geolocation geofence
⚡ Attack Vector
Victim plugs cable in to charge phone; attacker connects via Wi-Fi from the parking lot and injects commands to install keylogger.
🛡️ Defense / Mitigation
Use USB "data condoms" (power-only adapters), strict company ban on untrusted cables, implement endpoint USB behavioral telemetry.
08 Hardware Ethernet Tap
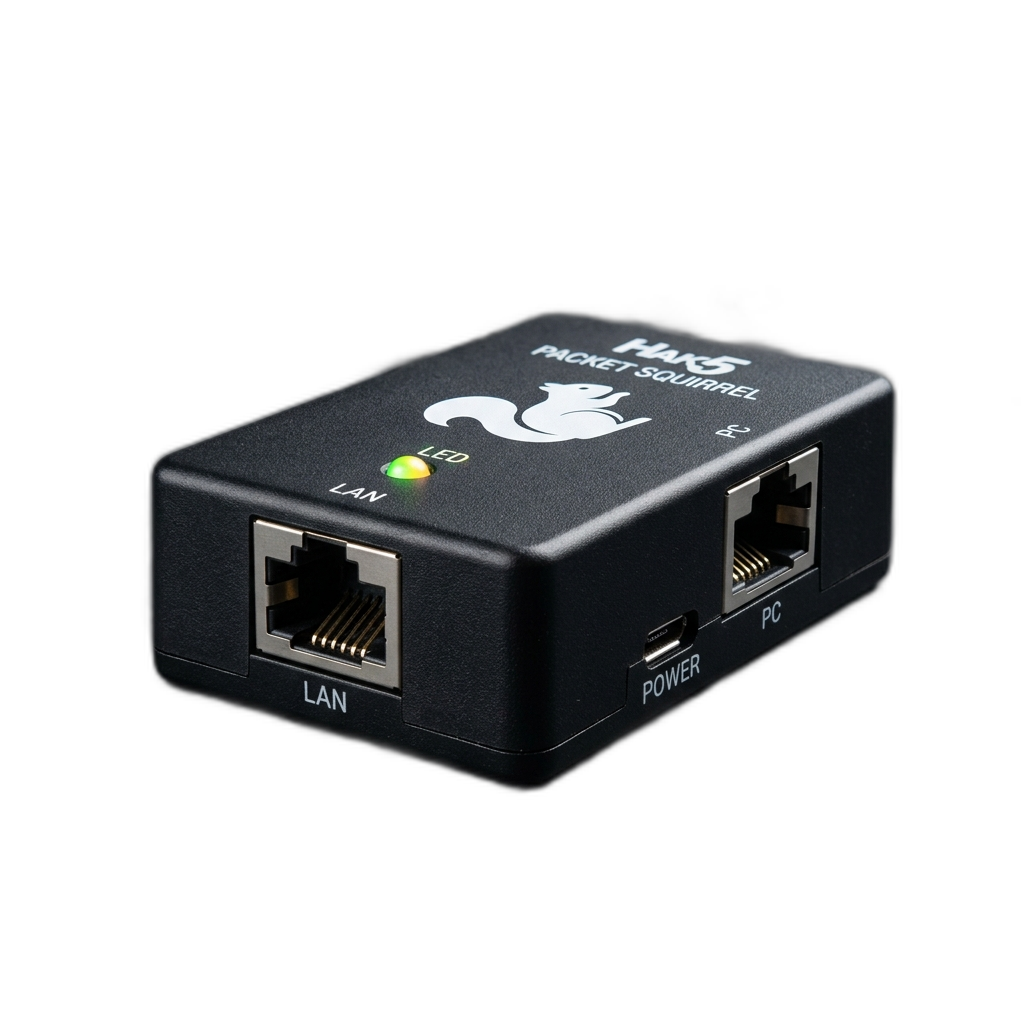
🌐 3D 360° ModelPacket Squirrel

Packet Squirrel

// Hak5
Capture & replay packets. Traffic analysis made easy.

Pocket-sized hardware Ethernet tap designed for inline packet analysis, automated network sniffing, and secure remote VPN tunneling. Powered by OpenWrt, it sits transparently between network cables. Flipping a 4-position physical switch automatically logs raw PCAP files directly to an attached USB thumb drive or initiates OpenVPN tunnels.
Network IO: Dual 10/100 Ethernet Ports (Transparent Bridge)
Automation: 4-Way Push Switch Payload Selection
Storage: Direct USB Mass Storage PCAP Logging
⚡ Attack Vector
Installed inline between printer/VoIP phone and wall jack; captures all unencrypted VoIP audio streams and print job contents.
🛡️ Defense / Mitigation
Enforce TLS 1.3 / SRTP encryption on internal network communications; enable Dynamic ARP Inspection (DAI) and IP Source Guard.
09 Professional RFID & NFC
🌐 3D 360° ModelProxmark3

Proxmark3

// RRG / RFIDler
RFID hacking tool for professionals. Hack RFID like a pro.

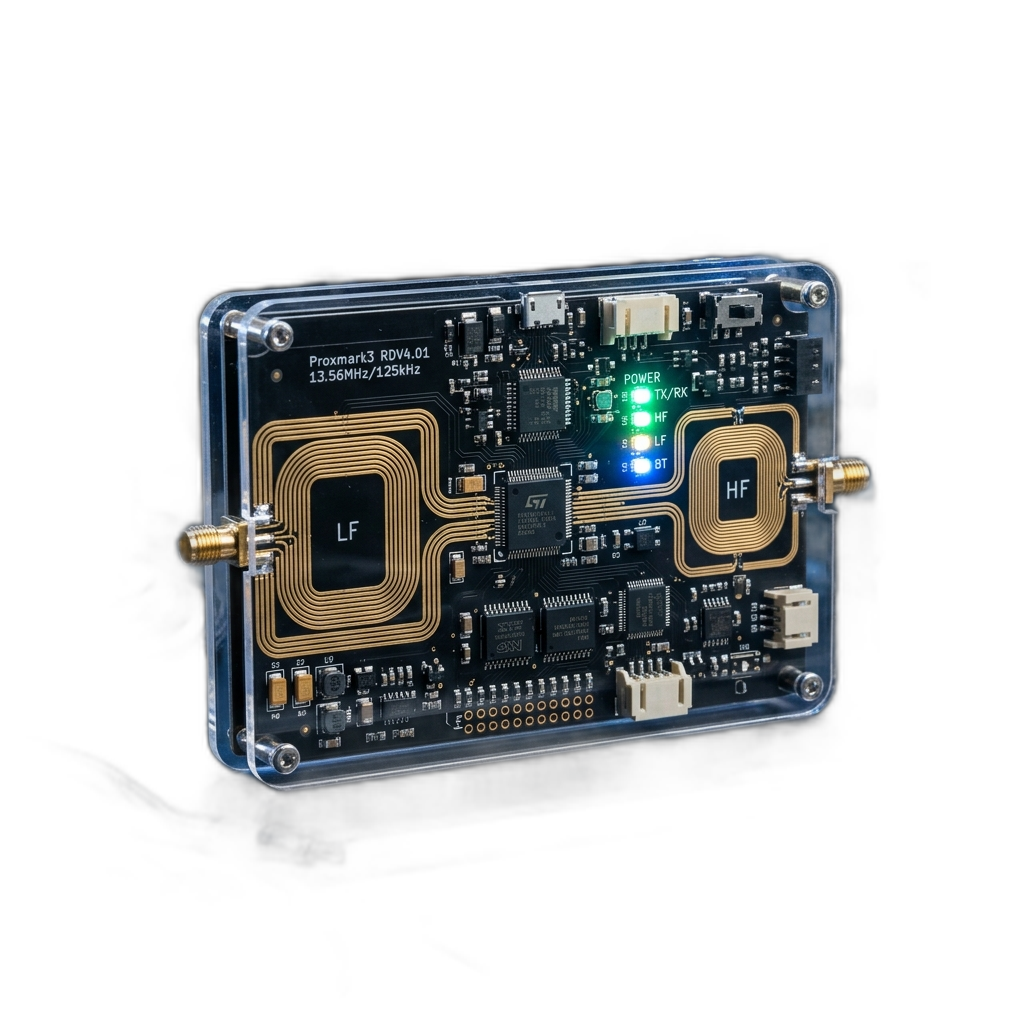
The industry gold standard dedicated to RFID/NFC protocol exploration and physical access exploitation. Supports dual-frequency: Low Frequency (125 kHz: EM410x, Indala, HID Prox) and High Frequency (13.56 MHz: Mifare Classic, Ultralight, iCLASS). Can sniff radio exchanges between cards and readers, simulate badges, and crack crypto keys via Darkside and Nested algorithms.
Frequencies: 125 kHz (LF) + 13.56 MHz (HF) Dual-Antenna
Cracking Engine: Darkside, Nested, Hardnested Cryptanalysis
Emulation: Tag Simulation, Reader Sniffing & Cloning
⚡ Attack Vector
Bumps into employee in hallway; reads card serial number; cracks weak Mifare keys; writes clone to rewritable T5577 card to enter facility.
🛡️ Defense / Mitigation
Deprecate unencrypted 125 kHz RFID badges and Mifare Classic; migrate to AES-128 encrypted Mifare DESFire EV2/EV3 or HID Seos.
10 Captive Portal Attack Framework
🌐 3D 360° ModelEvil Portal

Evil Portal

// Open Source / PineAP
Captive portal attack framework. Create fake login pages.

A modular captive portal attack framework deployed on rogue access points (WiFi Pineapple, ESP8266 Deauther, ESP32, or Raspberry Pi). Forces victims joining the rogue network into a walled garden where all DNS traffic redirects to a realistic login page imitating airport Wi-Fi, hotel portals, Starbucks terms, or corporate Google/Microsoft SSO logins.

Platform: WiFi Pineapple, ESP32, Linux AP Daemon
Mechanism: DNS Spoofing (Captive Portal RFC 7710/8908)
Payload: Cloned Google, Microsoft 365, WPA2 Passphrase Phish
⚡ Attack Vector
Sends deauth frames kicking users off coffee shop Wi-Fi; users reconnect to rogue twin; enter email password to regain internet.
🛡️ Defense / Mitigation
Never enter real credentials or passwords on public Wi-Fi splash pages; use cellular hotspots; require hardware security keys (FIDO2).
01

Shodan

IoT & Devices
https://www.shodan.io
IoT device search engine. Search internet-connected webcams, routers, servers & ICS systems.
Deep Recon Triage: Crawls the entire IPv4 space 24/7 collecting service banners. Find unpatched Apache, open SCADA/Modbus controllers, MQTT brokers, and default router logins. Use filters like port:22 country:IN org:"ISP".
02

Censys

Asset Discovery
https://censys.io
Internet infrastructure and attack surface discovery platform.
Deep Recon Triage: Built by the team behind ZMap at the University of Michigan. Correlates TLS/SSL certificates with host IP addresses. Essential for discovering origin IP behind Cloudflare WAF by searching for the target's SSL certificate fingerprints.
03

ZoomEye

Cyberspace Devices
https://www.zoomeye.org
Cyberspace search engine for network devices, industrial systems & web daemons.
Deep Recon Triage: Developed by Knownsec. Exceptional coverage of Asian and European cyberspace infrastructure, mapping web applications, camera streams, databases, and OS fingerprints with deep component version indexing.
04

GreyNoise

Threat Intelligence
https://www.greynoise.io
Internet noise, mass scanners, benign worms & adversary threat intelligence.
Deep Recon Triage: Separates background internet scanning noise (Shodan, Censys, mass Mirai bots) from targeted zero-day attacks against your network. Identifies whether an IP hitting your firewall is "internet noise" or a persistent adversary.
05

ONYPHE

Cyber Defense
https://www.onyphe.io
Cyber defense search engine and open-source attack surface discovery provider.
Deep Recon Triage: Specializes in passive cyber defense intelligence, mapping DNS, forward/reverse WHOIS, ports, SSL certificates, honeypot captures, and threat feeds into an integrated searchable asset index for security analysts.
06

BinaryEdge

Threat Intel Platform
https://www.binaryedge.io
Threat intelligence data platform scanning the global internet surface.
Deep Recon Triage: Scans the entire internet measuring exposures, misconfigured open databases (Elasticsearch, MongoDB), exposed RDP endpoints, vulnerability risk metrics, and DNS threat feeds for enterprise external attack surface management.
07

FOFA

Cyberspace Mapping
https://www.fofa.info
Cyberspace asset mapping engine with advanced query syntax.
Deep Recon Triage: Massive cyberspace search engine popular in bug bounties and Red Teaming. Exceptional for querying HTML title hashes, favicon mmh3 hashes, certificate subject names, and specific protocol banners to find hidden company portals.
08

LeakIX

Information Leaks
https://leakix.net
Information leaks search engine indexing exposed web services & misconfigurations.
Deep Recon Triage: The premier search engine for unauthenticated database leaks, exposed .env files, public Git repositories (.git/HEAD), open Elasticsearch clusters, and unprotected Redis instances on the public internet.
09

Criminal IP

Asset Inventory & Risk
https://www.criminalip.io
Cyber threat intelligence search engine for asset inventory and risk assessment.
Deep Recon Triage: Scans global IP addresses and domain reputations in real time. Analyzes malicious bots, phishing domains, open vulnerabilities, and compromised credentials with instant 5-tier risk severity ratings.
10

Netlas.io

Attack Surface Discovery
https://netlas.io
Attack surface discovery and global IP/domain protocol reconnaissance platform.
Deep Recon Triage: Provides rich multi-protocol scanning across HTTP, FTP, SMTP, SSH, and RDP. Features powerful boolean search operators to discover IP perimeters, WHOIS records, SSL SAN certificates, and IoT peripherals.
11

DeHashed

Leaked Credentials
https://www.dehashed.com
Leaked credentials search engine indexing breached passwords & user accounts.
Deep Recon Triage: Search across billions of compromised data breach records by email, username, IP, name, phone, or password hash. Critical for enterprise credential stuffing defense audits and corporate credential exposure monitoring.
12

SecurityTrails

DNS & Domains
https://securitytrails.com
DNS and domain data platform with historical A/MX/NS/SOA tracking.
Deep Recon Triage: Unmatched historical DNS database. Allows security analysts to see past IP addresses of a website before Cloudflare was enabled, revealing old origin servers, abandoned subdomains, and historical WHOIS owners.
13

DorkSearch

Google Dork Tool
https://www.dorksearch.com
Fast Google Dorking search engine with pre-compiled GHDB vulnerability queries.
Deep Recon Triage: Automated Google Dorking interface. Offers 1-click execution for thousands of curated dork templates targeting exposed admin panels, open cameras, leaked cloud keys, SQL errors, and unauthenticated web interfaces.
14

Exploit-DB

Exploit Archive
https://www.exploit-db.com
Official Offensive Security exploit and vulnerability proof-of-concept archive.
Deep Recon Triage: The ultimate CVE proof-of-concept (PoC) repository and home of the Google Hacking Database (GHDB). Maintained by OffSec, providing working Python, C, and Ruby exploit code for validated software vulnerabilities.
15

Pulsedive

Threat Intel Search
https://pulsedive.com
Community-driven threat intelligence search engine & IOC aggregator.
Deep Recon Triage: Consolidates indicators of compromise (IOCs), malicious IPs, compromised domains, and threat actor feeds. Generates real-time risk scores with historical infrastructure graphs and threat attribution badges.
16

GrayhatWarfare

Public S3 Buckets
https://grayhatwarfare.com
Public S3 buckets and cloud storage file search engine.
Deep Recon Triage: Continuously indexes millions of publicly accessible AWS S3 buckets, Azure Blobs, and DigitalOcean Spaces. Find exposed customer backups, database exports, invoices, and source code archives by searching company keywords.
17

PolySwarm

Threat Marketplace
https://polyswarm.io
Crowdsourced decentralized threat detection and malware marketplace.
Deep Recon Triage: A multi-engine threat detection ecosystem where specialized cybersecurity companies compete with custom AI engines to detect emerging zero-day malware, suspicious payloads, and novel malicious files.
18

URLScan.io

Website Analysis
https://urlscan.io
Website and URL scanning sandbox with DOM tree & network inspector.
Deep Recon Triage: Safely renders target websites in a secure browser sandbox. Records DOM elements, screenshot previews, outgoing HTTP requests, third-party JavaScript trackers, loaded certificates, and redirects to uncover hidden phishing sites.
19

Vulners

Vuln Database
https://vulners.com
Real-time vulnerability database and CVE correlation search engine.
Deep Recon Triage: The Wikipedia of security vulnerabilities. Aggregates NVD CVEs, vendor advisories, bug bounty write-ups, and public Metasploit modules into a unified search index with CVSS v3.1 scoring and patch links.
20

Wayback Machine

Web Archive
https://archive.org/web/
Historical web page archive preserving internet snapshots since 1996.
Deep Recon Triage: Inspect historic versions of target websites to find deprecated API endpoints, old employee directories, forgotten staging portals, old copyright notices with legal entity names, and removed documentation.
21

crt.sh

Certificate Transparency
https://crt.sh
Certificate Transparency log search engine for instantaneous subdomain discovery.
Deep Recon Triage: Every public SSL/TLS certificate issued must be logged to immutable CT logs. Searching %.target.com instantly reveals every subdomain ever granted an SSL cert, including internal staging and VPN endpoints.
22

WiGLE.net

Wireless Mapping
https://wigle.net
Global wireless network mapping platform with GPS geotagged BSSIDs.
Deep Recon Triage: World's largest crowdsourced database of wireless networks, cell towers, and Bluetooth devices. Query by SSID or MAC/BSSID to pinpoint the physical geographic GPS coordinates of an organization's wireless routers.
23

PublicWWW

Source Code Search
https://publicwww.com
Source code search engine indexing HTML, JavaScript, CSS & web page assets.
Deep Recon Triage: Search directly within the HTML, JS, and CSS source code of millions of websites. Find websites sharing identical Google Analytics IDs, unique JavaScript API keys, malicious web skimmers, or specific CMS widgets.
24

Hunter.io

Email Discovery
https://hunter.io
Professional email address finder and corporate pattern discovery tool.
Deep Recon Triage: Scrapes the web to identify email address patterns for any domain (e.g. {first}.{last}@target.com). Lists verified employee emails with public sources, invaluable for authorized phishing tests and employee recon.
25

Intelligence X

OSINT & Breaches
https://intelx.io
OSINT search engine indexing darknet leaks, paste sites & data breaches.
Deep Recon Triage: Archives raw historical data from paste sites, Tor hidden services, Telegram breach channels, and whois records. Preserves full raw records even after the original pastebin or onion leak site is taken down.
26

Grep.app

Code Search (GitHub)
https://grep.app
High-speed code search engine across 500,000+ public GitHub repositories.
Deep Recon Triage: Blazing-fast regex code search across half a million git repositories. Perfect for finding how developers implement proprietary APIs, hardcoded secret tokens, dangerous functions (eval, exec), or vulnerable dependencies.
27

Packet Storm

Security Tools & Exploits
https://packetstormsecurity.com
Comprehensive security tools, advisories, zero-day research & exploit repository.
Deep Recon Triage: Legendary cybersecurity clearinghouse active since 1998. Features daily security news, full-disclosure vulnerability advisories, custom whitepapers, penetration testing tools, and functional exploit scripts.
28

Searchcode

Source Code & API
https://searchcode.com
Comprehensive source code and API search engine across multiple code repositories.
Deep Recon Triage: Searches over 75 billion lines of code across GitHub, Bitbucket, GitLab, Google Code, and SourceForge. Filter by programming language to locate API documentation, cryptographic routines, and configuration files.
29

DNSDB

Historical DNS Data
https://www.dnsdb.info
Historical passive DNS data search engine by Farsight Security.
Deep Recon Triage: The world's largest passive DNS database. Captures raw resolution queries from real internet recursors to reconstruct historical domain mappings, identify fast-flux botnets, and trace threat actor command-and-control servers.
30

FullHunt

Asset Discovery
https://fullhunt.io
Modern attack surface discovery platform and corporate perimeter mapper.
Deep Recon Triage: Continuously monitors corporate perimeters for exposed assets, unpatched software, and security misconfigurations. Features automated asset discovery with rich API integration for threat intelligence automation.
31

VirusTotal

Malware Analysis
https://www.virustotal.com
Malware analysis, file scanning & URL reputation engine with 70+ AV scanners.
Deep Recon Triage: Scans files, hashes (MD5/SHA256), and URLs across 70+ major antivirus engines. Displays behavioral sandbox execution reports, network communications, dropped files, and community threat actor tags.
32

DNSDumpster

DNS Recon Tool
https://dnsdumpster.com
Free domain research tool discovering subdomains, MX records & network graphs.
Deep Recon Triage: The go-to tool for fast passive DNS reconnaissance. Maps DNS records (A, MX, NS, TXT) and generates an interactive visual topology map showing IP subnet clustering and mail/DNS hosting providers.
COPIED TO CLIPBOARD